Blog
Elliptic Curve Cryptography Tutorial

We invite you to read this article for a more detailed introduction to ECC encryption and to discover why it’s set to turn out to be the next internet normal in its field. This takes us to another realm of arithmetic, arguably extra abstract that prime quantity factorization that underpins the RSA algorithm. However ECC is fascinating in its own proper and supplies security safety than RSA. Though not in widespread use as of at present, ECC is the future of public-key cryptography. For rigorously chosen (by cryptographers) finite fields and elliptic curves, the ECDLP drawback has no environment friendly solution.
For The Love Of Prime Numbers-part 2
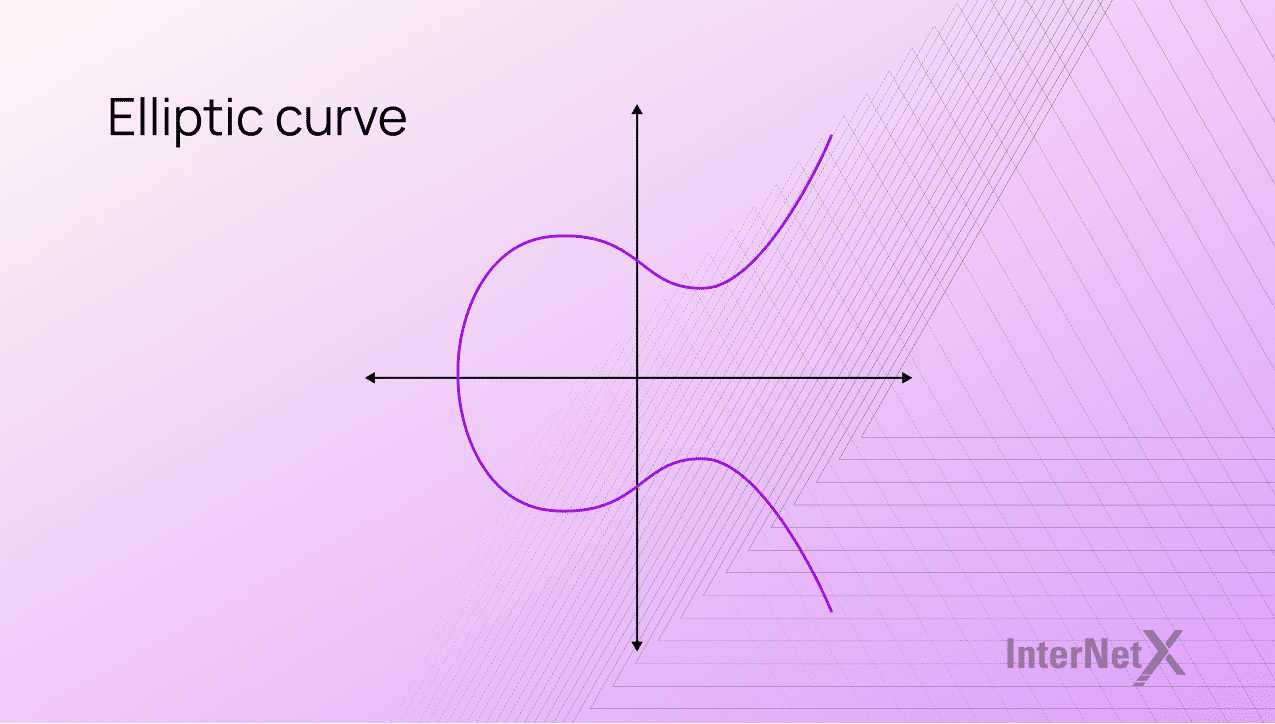
An elliptic curve is not only a reasonably picture, it also has some properties that make it an excellent setting for cryptography. After the introduction of RSA and Diffie-Hellman, researchers explored different mathematics-based cryptographic options on the lookout for different algorithms beyond factoring that may function good Trapdoor Features. In 1985, cryptographic algorithms have been proposed primarily based on an esoteric branch of arithmetic referred to as elliptic curves. These factoring algorithms get more environment friendly as the scale of the numbers being factored get bigger. The gap between the issue of factoring giant numbers and multiplying massive numbers is shrinking as the number (i.e. the key’s bit length) gets larger.
Even with the above cautions, the benefits of elliptic curve cryptography over conventional RSA are broadly accepted. Many experts are involved that the mathematical algorithms behind RSA and Diffie-Hellman might be damaged within 5 years, leaving ECC as the one affordable different. ECDHE stands for Elliptic Curve Diffie Hellman Ephemeral and is a key trade mechanism primarily based on elliptic curves. This algorithm is used by CloudFlare to offer good forward secrecy in SSL. The RSA part means that RSA is used to prove the id of the server. Take the prime numbers 13 and 7, their product offers us our maximum worth of 91.
E Mail Safety
You can examine zkSNARKs in our weblog, “Zero-Knowledge Proofs – Understanding zkSNARKs”. ECC considerably enhances cellular and IoT device security by delivering sturdy encryption with minimal computational overhead, decreased battery consumption, and quicker processing speeds in comparison with conventional cryptographic strategies. Your personal key is a big random number, which when multiplied with a base point, sometimes also called generator level, on the curve yields your public key. The infeasibility of performing division on the elliptic curve known as the discrete logarithm downside or sometimes also referred to as the elliptic curve discrete logarithm downside (ECDLP). In the final case, keep in mind that Curve25519 is faster than secp256k1 and the opposite 256-bit standard NIST curves and is considered safer, so it is the really helpful selection for ~ 128-bit security. Equally, the Curve448 has higher efficiency than the classical curves with comparable key size, so it is the beneficial curve for ~ 224-bit safety.
Time Lock Puzzles And Timed Launch Cryptography – Trendy Methods
Using elliptic curve cryptography saves time, energy and computational sources for each the server and the browser helping us make the online each faster and more secure. The ECC is quicker than the other two types as a result of the key sizes are smaller and consume less https://www.internetling.com/category/programming/programming-software power. It ends in sooner encryption and decryption, making ECC most applicable to be used the place excessive performance calls for encompass cell units and IoT gadgets.
- Remodeling the principles described above into a set of equations could seem easy, but actually it might be actually tedious as a outcome of it requires fixing cubic equations.
- The second use for ECC is in the course of the handshake when the Internet server and consumer are negotiating session keys that are used to encrypt the entire knowledge sent between the server and browser.
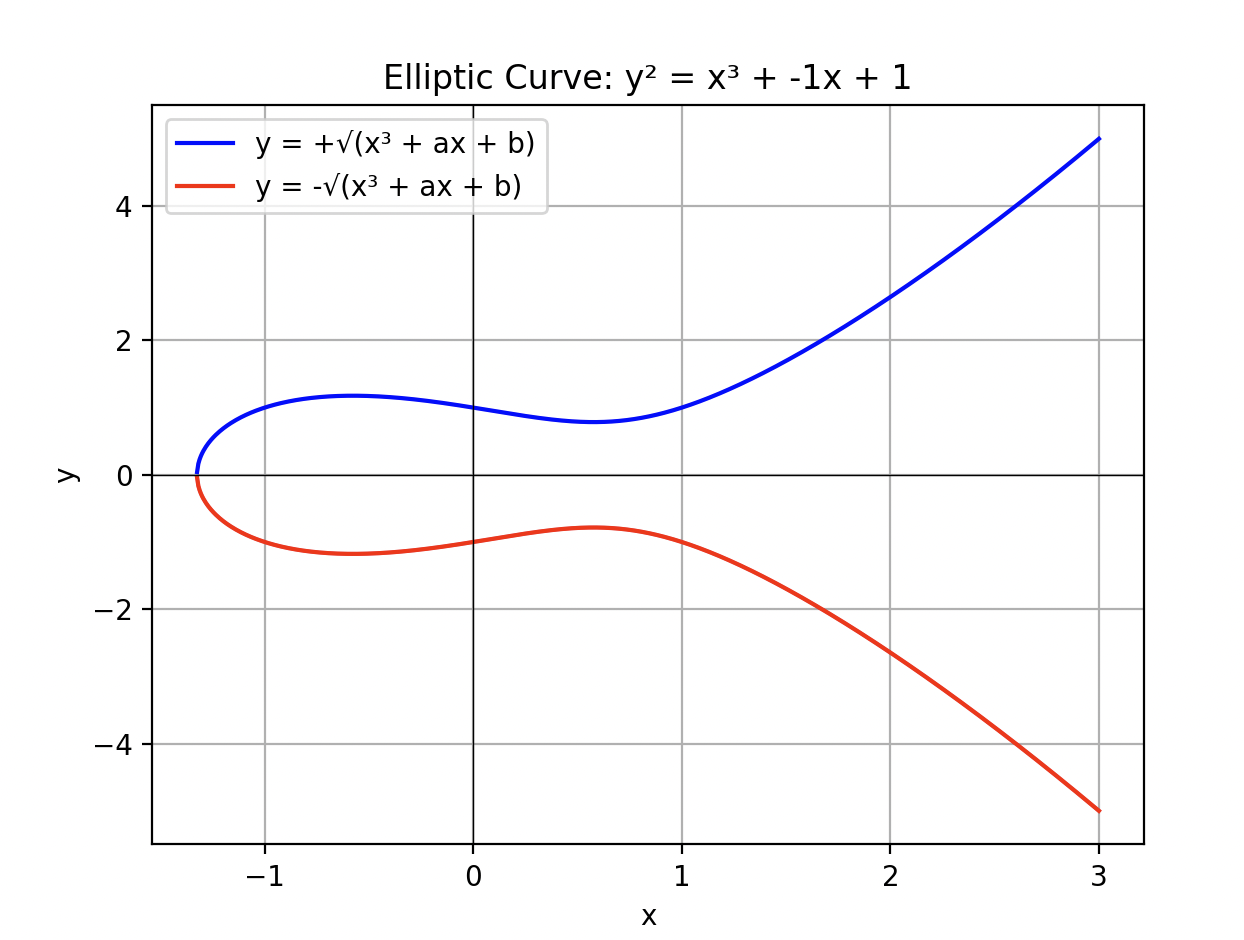
- Whereas all this would possibly sound very complex at first you will see shortly that a graphical strategy is sufficient to develop an intuition for the math used on elliptic curves.
- But ECC is fascinating in its personal right and provides security security than RSA.
- ECC vulnerabilities include weak curve parameters, side-channel attacks, implementation flaws, quantum computing threats, and invalid curve assaults.
- In order to know what’s written right here, you’ll need to know some fundamental stuff of set principle, geometry and modular arithmetic, and have familiarity with symmetric and asymmetric cryptography.
Hardware functionality and safety requirements are major https://repairdesign24.com/decor/how-to-make-a-bootable-flash-drive.html considerations while implementing secure key storage and key administration, particularly in resource-constrained environments. Whereas ECC, in general, offers higher performance compared to extra conventional public-key techniques, there are vital challenges in efficiently implementing it without sacrificing security. High-performance implementations typically require specialty optimizations concentrating on different platforms and use cases.

In the end, we are able to compute $151 \cdot P$ performing just seven doublings and four additions. For our goals, we may also need some extent at infinity (also known as best point) to be a half of our curve. From now on, we are going to denote our level at infinity with the image 0 (zero). Avoid expired certificates, name mismatches, and different safety points with Trusted Automated SSL certificates to keep your web site safe and working smoothly. If you might have a web site that requires powerful safety and is complex, ECC might be the proper match for you.
Before ECC turn out to be popular, almost all public-key algorithms were primarily based on RSA, DSA, and DH, different cryptosystems based mostly on modular arithmetic. RSA and associates are nonetheless crucial today, and infrequently are used alongside ECC. Nevertheless, while the magic behind RSA and friends may be easily defined, is extensively understood, and rough implementations could be written fairly easily, the foundations of ECC are still a thriller to most. We know that the keys produced by ECC are smaller in length and quicker to generate. On the opposite hand, when RSA keys reach the length of 3072-bits or over, ECC performs over one hundred pc quicker. ECC presents the same degree of safety as those regular algorithms similar to RSA however with compressed keys.
Why is Elliptic Curve Cryptography (ECC) popular right now, and why did it evolve? Firstly ECC is a public key cryptosystem identical to RSA who got here earlier than it. ECC was designed and developed to beat a weakness of the RSA algorithm, being Index Calculus. Index Calculus is fancy ‘math word speak’ for a type or group of sieve algorithms that makes use of mathematical processes to cut back the hardness of the computation of prime quantity factorisation and thus decease or destroy the effectivity of RSA. In 1985 a mathematician by the name of Victor Miller looked at elliptic curves in cryptography and hypothesized it could be extraordinarily unlikely the index calculus method would ever work in respect of Elliptic Curves.